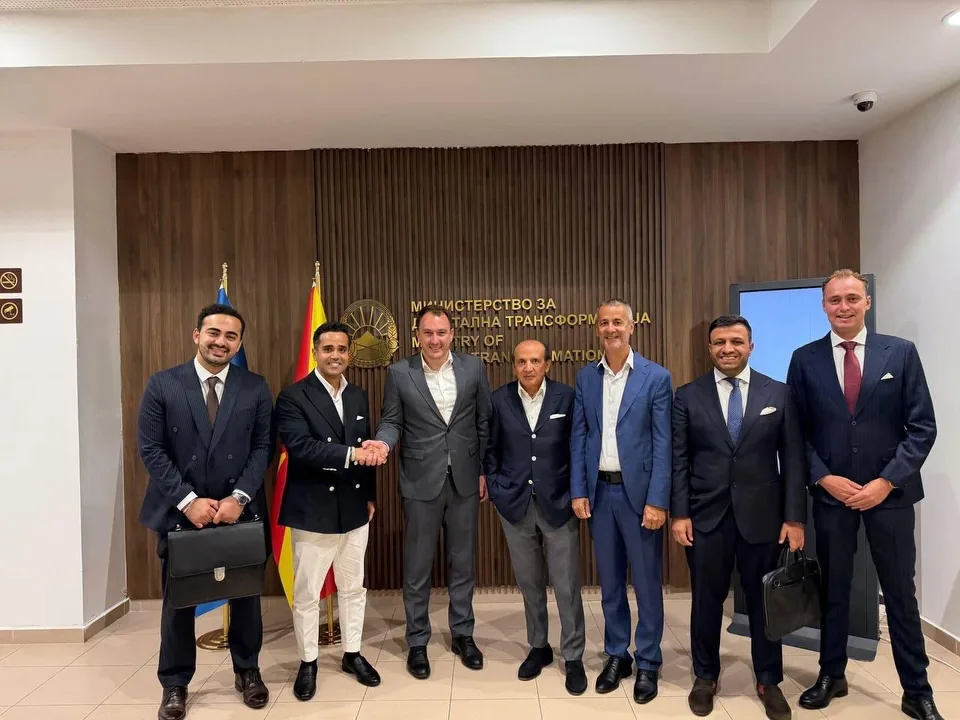
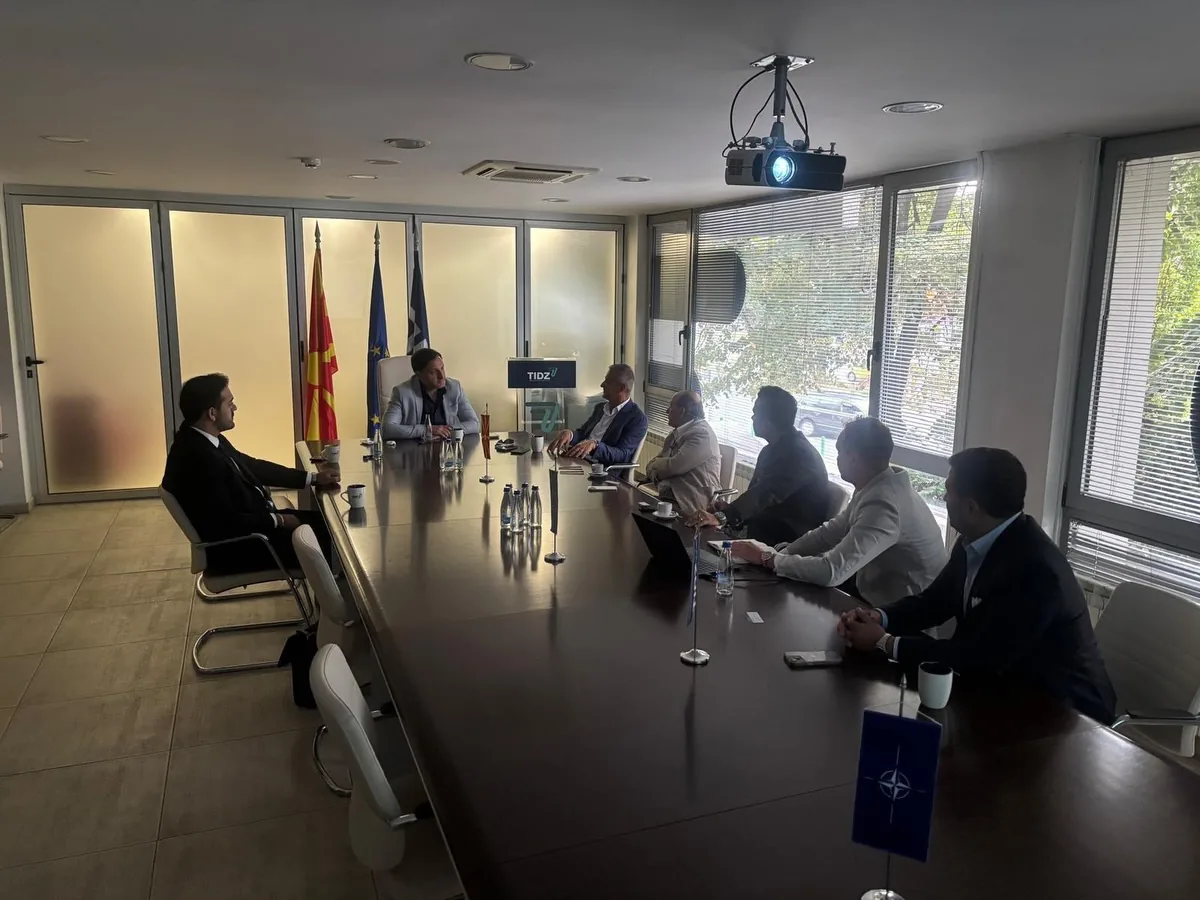
Our co-founder and CEO Abdussamed Nazik was part of a delegation to North Macedonia. Talks with the Minister of Digital Transformation and Invest North Macedonia focused on AI and secure digital infrastructure.
Instagram
Posts
germanaidefense
germanaidefenseNorth Macedonia | Strategic Dialogue on AI and Digital Infrastructure
Our Co-Founder and CEO, Abdussamed Nazik, was part of a delegation to North Macedonia together with Hadi Teherani, Payam Hazin, Nihat Yilmaz and Fabian Weber, accompanied by Prof. Orce Simov. We met with H.E. Stefan Andonovski, Minister of Digital Transformation, and Goce Dimovski, Director of Invest North Macedonia.
North Macedonia | Strategic Dialogue on AI and Digital Infrastructure
Our Co-Founder and CEO, Abdussamed Nazik, was part of a delegation to North Macedonia together with Hadi Teherani, Payam Hazin, Nihat Yilmaz and Fabian Weber, accompanied by Prof. Orce Simov.
We met with H.E. Stefan Andonovski, Minister of Digital Transformation, and Goce Dimovski, Director of Invest North Macedonia to discuss concrete opportunities for cooperation between North Macedonia and Germany in artificial intelligence, digital transformation and energy infrastructure.
A key topic was the vision for an AI Innovation Park that brings together artificial intelligence, energy and secure digital infrastructure within one ecosystem. The goal is to create sustainable economic value and strengthen North Macedonia as an investment destination.
We would like to thank Minister Andonovski and Goce Dimovski for the open and forward-looking exchange.
At GermanAI Defense, we contribute our expertise in artificial intelligence, cybersecurity and secure digital infrastructure. From dialogue to implementation, step by step.
#NorthMacedonia #Germany #ArtificialIntelligence #DigitalInfrastructure #Cybersecurity #GermanAIDefense… more
North Macedonia | Strategic Dialogue on AI and Digital Infrastructure
Our Co-Founder and CEO, Abdussamed Nazik, was part of a delegation to North Macedonia together with Hadi Teherani, Payam Hazin, Nihat Yilmaz and Fabian Weber, accompanied by Prof. Orce Simov.
We met with H.E. Stefan Andonovski, Minister of Digital Transformation, and Goce Dimovski, Director of Invest North Macedonia to discuss concrete opportunities for cooperation between North Macedonia and Germany in artificial intelligence, digital transformation and energy infrastructure.
A key topic was the vision for an AI Innovation Park that brings together artificial intelligence, energy and secure digital infrastructure within one ecosystem. The goal is to create sustainable economic value and strengthen North Macedonia as an investment destination.
We would like to thank Minister Andonovski and Goce Dimovski for the open and forward-looking exchange.
At GermanAI Defense, we contribute our expertise in artificial intelligence, cybersecurity and secure digital infrastructure. From dialogue to implementation, step by step.
Daily headlines from recognized security sources, collected automatically and updated continuously. Tap any item to read the full report at the source.
Loading latest reports…
·
Headlines and short excerpts belong to their respective source and link there. No liability for third-party content.